
MIT TRACE
Global Supply Chain Cybersecurity Observatory
An intelligence observatory that discovers, organizes, and profiles cyber incidents with real-world impact across logistics, manufacturing, transportation, and global supply chains.
Detects global signals
Tracks public reports, open sources, and operational impact patterns.
Structures the incidents
Turns scattered findings into comparable, auditable incident profiles.
Prioritizes decisions
Helps technical and executive teams understand operational risk.
Who is Behind MIT TRACE?
MIT TRACE is shaped by international collaborators connecting cybersecurity research, supply chain risk, and data-driven incident intelligence
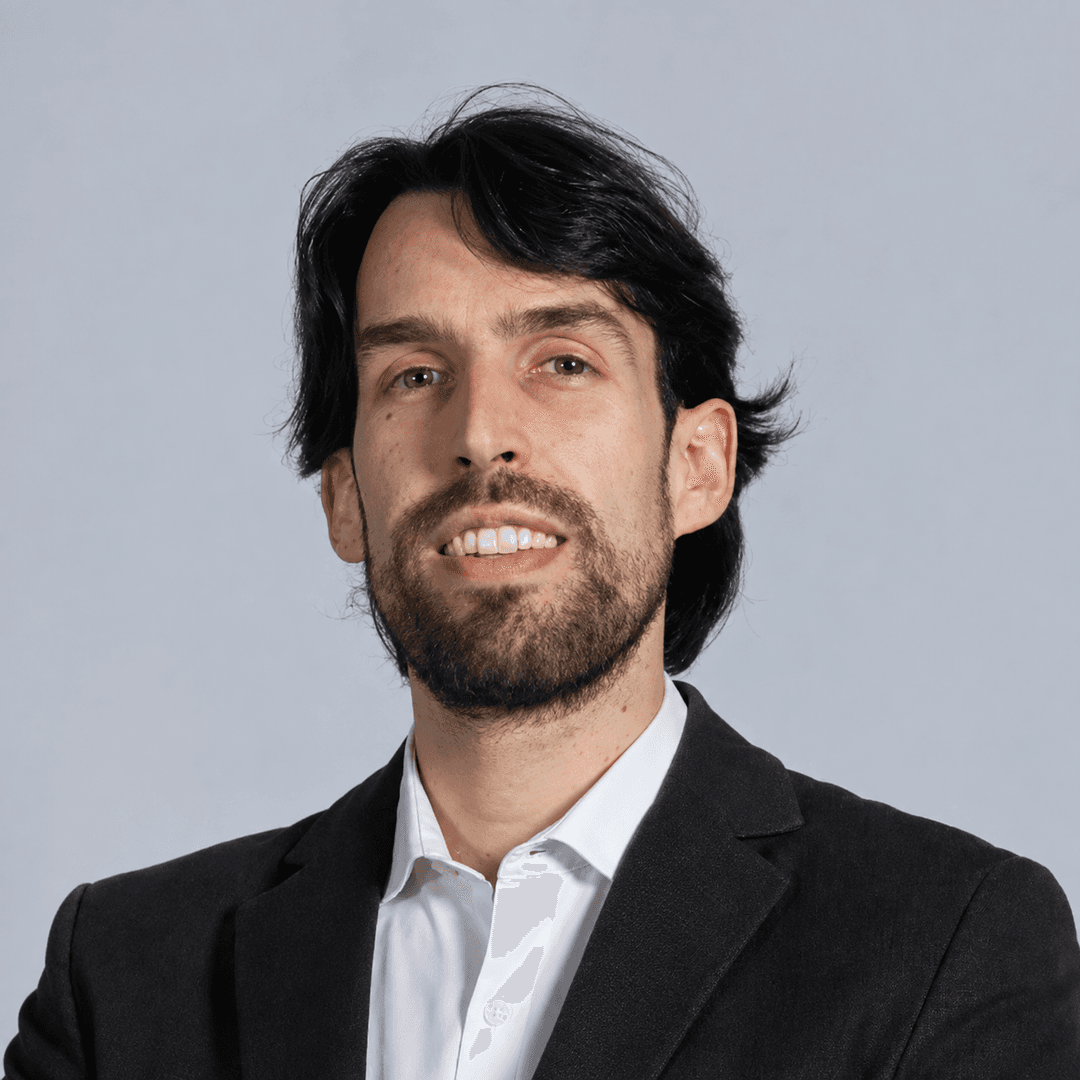
Miguel Rodríguez
Research Scientist
Co-Founder & Director, Supply Chain Cybersecurity Lab

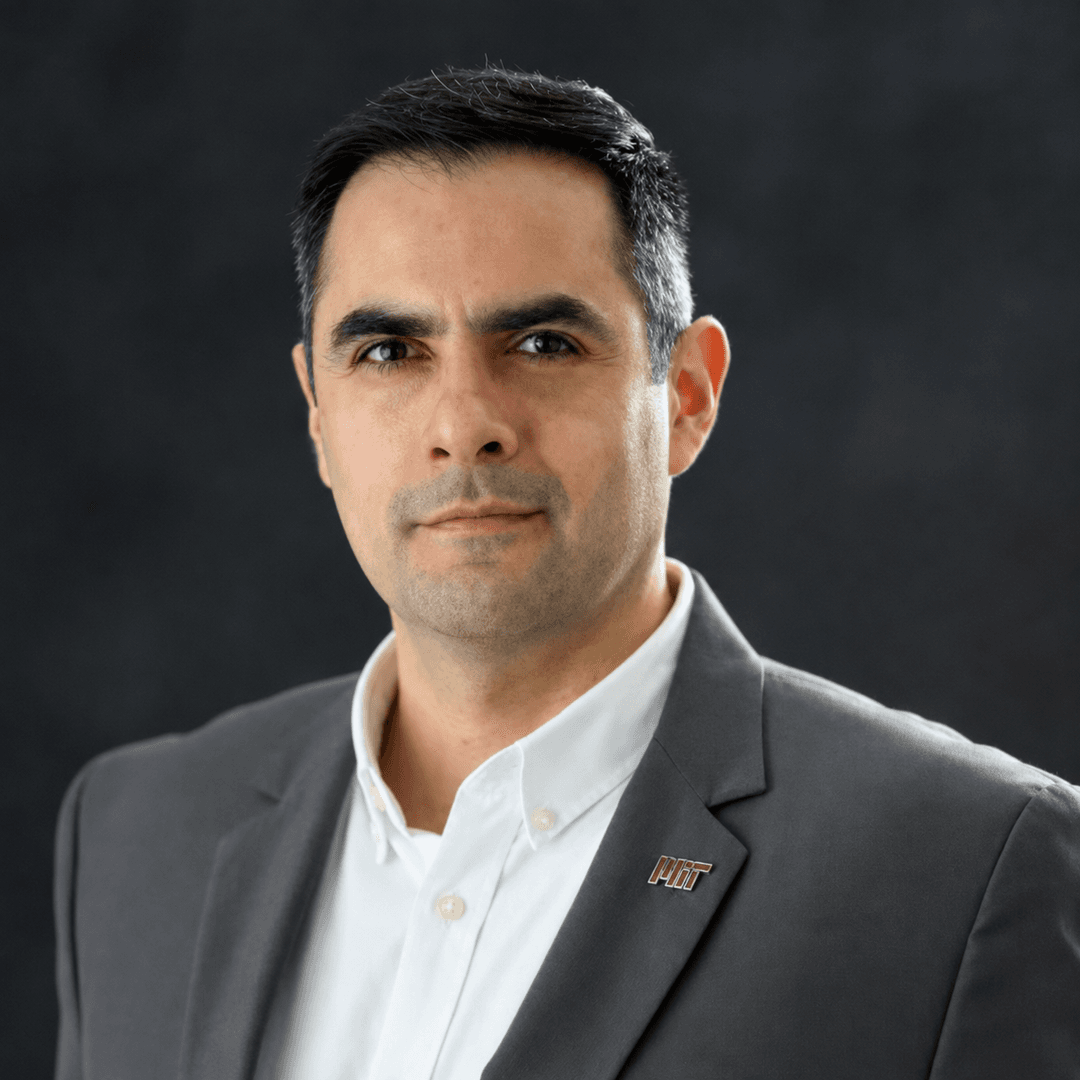
Camilo Mora
Postdoctoral Associate
Co-Founder, Supply Chain Cybersecurity Lab
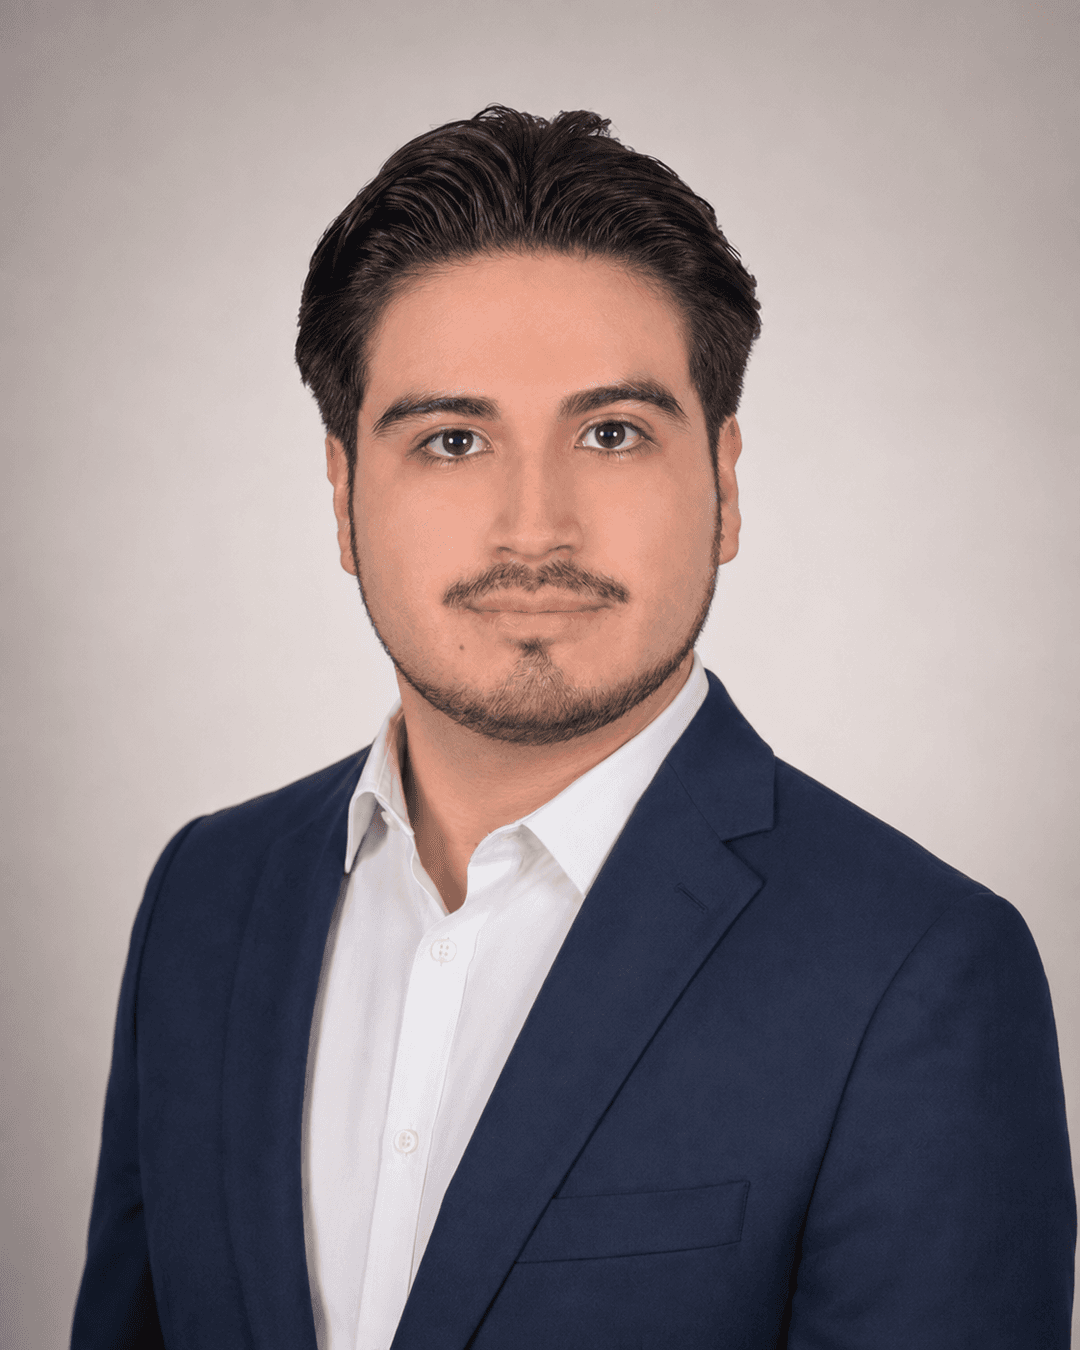
Alonzo Estévez
Computer Technologies Engineer
MIT TRACE Principal Full-Stack Developer
Analyze Cyber Risks Connections
When an intrusion compromises digital assets, the consequences can surface in inventory, routing, production, delivery times, and business continuity. MIT TRACE was built to make that connection visible.
Fragmented information
Incidents appear across news articles, disclosures, technical reports, and regional sources in inconsistent formats.
Physical impact is hard to measure
A digital attack can stop plants, ports, carriers, suppliers, and downstream operations.
Risk is distributed
Dependencies across companies and geographies can turn a local event into a global disruption.
Organizations do not only need to know that an attack happened. They need to understand where it happened, who was affected, what type of operation was disrupted, and how the event compares with others.
A simple flow for a complex problem
MIT TRACE combines search, assisted review, normalization, and visualization. You can feel like moving from a desk full of reports to an organized command center.
Explores open sources
Looks for public sources about incidents that matter to operations and supply chains.
Interprets context
Separates noise, duplicates, and weak mentions from events with meaningful evidence.
Normalizes findings
Organizes companies, countries, sectors, attack types, impacts, and sources into a shared format.
Preserves evidence
Keeps source traceability and structures the data so teams can review it later.
Delivers intelligence
Turns incident profiles into maps, charts, filters, and comparisons that support decisions.
Turning research into operational advantage
MIT TRACE does not replace expert judgment, it amplifies it. The platform organizes evidence, accelerates situational awareness, and helps teams prioritize where to look first.
Analytical speed
Reduces the time between discovering an event and understanding its operational relevance.
Comparable data
Standardizes incidents so teams can review trends, severity, sectors, and affected geographies.
Geographic insight
Locates impacts by country and region to connect digital risk with logistics exposure.
Supply chain visibility
Reveals relationships between companies, suppliers, sectors, and disruption types.
Executive language
Presents results through dashboards and narratives that technical and leadership teams can share.
Continuous improvement
A structured data foundation makes validation, enrichment, and deeper research easier over time.
Converting isolated incidents into a resilient perspective
MIT TRACE delivers clarity with a faster, more structured, and defensible way to understand how cyberattacks affect the physical world of supply chains.